GDPR is just a legal attempt at Y2k

Suddenly I realised, as one who profited handsomely (not in money but in perks’ way), that the whole GDPR compliance thingy is becoming quite similar, all too similar, to the hype that was called The Millennium Problem … too bad we now know how that ended, otherwise an illustrative movie could be made of the latter – now only (?) a documentary review is worthwhile, as history writing. Too bad it isn’t out in the open that despite all efforts then made, actually quite a lot of companies ended up having to hire temps to do all sorts of manual corrections in their administrations due to e.g., spreadsheets [the very things the toughest, most important business decisions hinged, and still hinge on!] going heywire over date fields.

To come back to the Issue … Are you not hit by that, almost sudden, avalanche of GDPR compliance warnings lately, like, the past couple of weeks ..? Is it not a warning that you need to do loads of things now, starting with hiring consultants (call to action; they’re Sales messages of course) this time not of the tech kind – engineers that see a problem, craft a solution and we’re done –, but of the legal kind – profiting only from prolongation of your insecurity.

And ah, there’s the snag! Multifaceted it is;

  • One: With some deadline suitably near to instill fear of lurking deadlines but suitably far to be able to still write you up with many, many ticks (per 6 or 3 minutes ..!?) at ridiculous rates, will be written;
  • Two: Unlike the patching that was the core solution (after Inventory – you did keep that in appropriate order in your wide-scope CMDB ever after 31/12/00, right ..? Even with some global outpost in the corner writing that down as 12/31/00. What stupid value loss if you didn’t! We’re only 17 years on! Did you really think legacy problems would have gone away by now …!?), we now see there is no solution but just getting compliant with all sorts of stupidly unprofitable, inefficient (and might we add, ineffective! yes if you are realistic, that’s what it is) good-for-nothing overhead;
  • Three: The good-for-nothing part — maybe not fully nothing, but oh so limitedly good for anything that you should’ve done already long ago not only for any ‘privacy’ compliance but for effective and efficient IT, -security included.

Following on this Lotus list, indeed there’s a lot of work to be done to become compliant … on the Legal side. On the IT side maybe also, but what needs to be done there, is (re)implementation of sound practices that should have been common daily practice anyway, and when implemented as such, ready; done.

The legal side on the other hand, sees all sorts of enduring challenges, like many cultural changes; no leaning back and await questions for advice to be answered out of hand with “It depends…” / “Come with a proposed solution and I’ll tell you whether it may or may not be permissible”, but for once being actively engaged and delivering definitive answers, and designing, implementing, and carrying out your (Legal) selves reams of procedural stuff. Acting on assessments, acting in communications, acting in control(s), etc.

You get it — the GDPR brings many problems for many organisations, the biggest of the problems being how to manage back the (Legal) consultancy fees… Remember, when data leakage isn’t preventable (as some dunces might still believe, many on the Legal side of GDPR compliance among them – hey they even think pseudonymisation amounts to anything), bad things are bound to happen. When (not if) not already via the avalanche of information requests …

I rest my case now, for you to have time to process the above, get it, and leave you with:

Your GDPR compliance looks much, much worse (this is actually quite good!); Toronto]

One 000

Yes, celebrations … The one-thousandestest post on this blog… [Excluding the two cross-posts by others…]

Do I regret any of them ..? Nope. [Rounded down]
Do I regret having been early with signalling many developments ..? Nope. At worst, sometimes I may have been too early, with the post(s) having slid from memory (ah, shallows you are) when finally the world came ’round to see the point as pointed out by some random stranger top-notch journalist or guru.
Non, je ne regrette rien.

OK, yes, I’ll keep on truckin’ for a while.
On everything from metaphilosophical discussions down to bitwise details on phenomena of Information, Society, IoT, Privacy, Information Security (#ditchcyber) Oxford, and gadgetry. Plus:
[The allusion to ‘reflection’ (of the old in the new etc.) is purely accidental, of course; London a decade ago]

Een pagina’tje met wat verzamelde links over/voor/inzake auditors/accountants

Gewoon, omdat het anders zo’n zoekwerk is met van die vervelend lange URLs…

Als de basiservaring niet meer kan worden opgedaan, dan …
Achterhaaldheid, v.v. veranderbereidheid
DACs en auditkantoren
Overbodigheid, achterhaaldheid weer
Assurance levels
AI, robots en auditwerk
Zucht, ja, blockchain
Process health
De markt
Multi-content assurance
XML-mogelijkheden
Direct reporting door accountants

GoTo Statement Considered Political

Bear with me; this is a mindstretcher.

Desperately few (still alive) have ever really fully read The Original (no, not that one).
And now I realise It (not it) was, and is, very valid today, as the opposite – at a meta(?)physical, quasi(?)(in)formal-logic level of abstraction – of what latter-day politicking looks like, in so many places around the world. Dangerous, that is, the latter.

Where the danger of GoTo is in its contextless jumping, ripping away the checks and balances that govern it, keep the oversight. In BASIC and others (JMP anyone?), at least there’s a form of kernel ‘hyperviser’/BIOS sort-a function, as underpinning foundation or supervisor to fall back to in last resort. [Yeah, I know one could program to wreck that but that’s not the point, and often disallowed by technical cast-in-concrete barriers.]
Where the danger of presidentiality-, morality- and common decency-less lies and alternative fact mumbo jumbo, is in its destruction of the checks and balances that govern that, keep the oversight. In reality, there’s no over/underpinning control mechanisms. They get destroyed.

’nuff said. And:
[Looks so real it’s ridiculous! But Fake!; Barça]

Golden Oldie Pic of the Day

Yet again …:

[Yes I, this refers to your infosec arrangements – wouldn’t deride the terms ‘management system’ or ‘practices’ by attaching them to what you do…]
[Yes II I did not include a dropcap style in his post on purpose. Thanks you noticed.]

Decision time for informational priv

When discussing Privacy, a lot of attention goes to informational privacy, easily tautologised with person-possibly-indentifying data.
If that reads mixed-up, it’s because it is.
But that’s for another session series. Of series.

What today’s post title is about, is the distinction between the two sides of the house; informational privacy (which is about information about you, or which you generate) versus decisional privacy (commonly defined in terms of your right to freely decide over your body’s integrity). As you read that, clearly the latter needs an update; a heck of a long KBxyzuvw article attached.
Because both the

  • Outright choice limitation through covert or overt profiling and covert or overt automated decision making, sometimes limiting your choice to none when you get rejected (from the ability to even decide) for something, or get no service proposition at all, a.k.a. the Hobson’s choice of socmed,
  • Covert choice limitation through filter bubbles – which would more accurately be called filter fish-trap,

can result from a lack of informational privacy. But both aren’t well covered in the definition of decisional priv whereas that infamous thing with The Freedom of the Pursuit of Happiness or whatsitcalled I don’t care you get it, Freedom, should be guaranteed.
So tightly coupled with all sorts of metaphysics, ontology, and topology of Privacy. Like, the feeling and understanding y’all have when you hear that word. It’s not only ‘bugger off nothing of your interest here’ privacy but also ‘get off my back‘ privacy; no weighing down.

Oh well. This being among my interests but not really my training, so I’ll go read up the latest qua this all. Pointers appreciated. And:
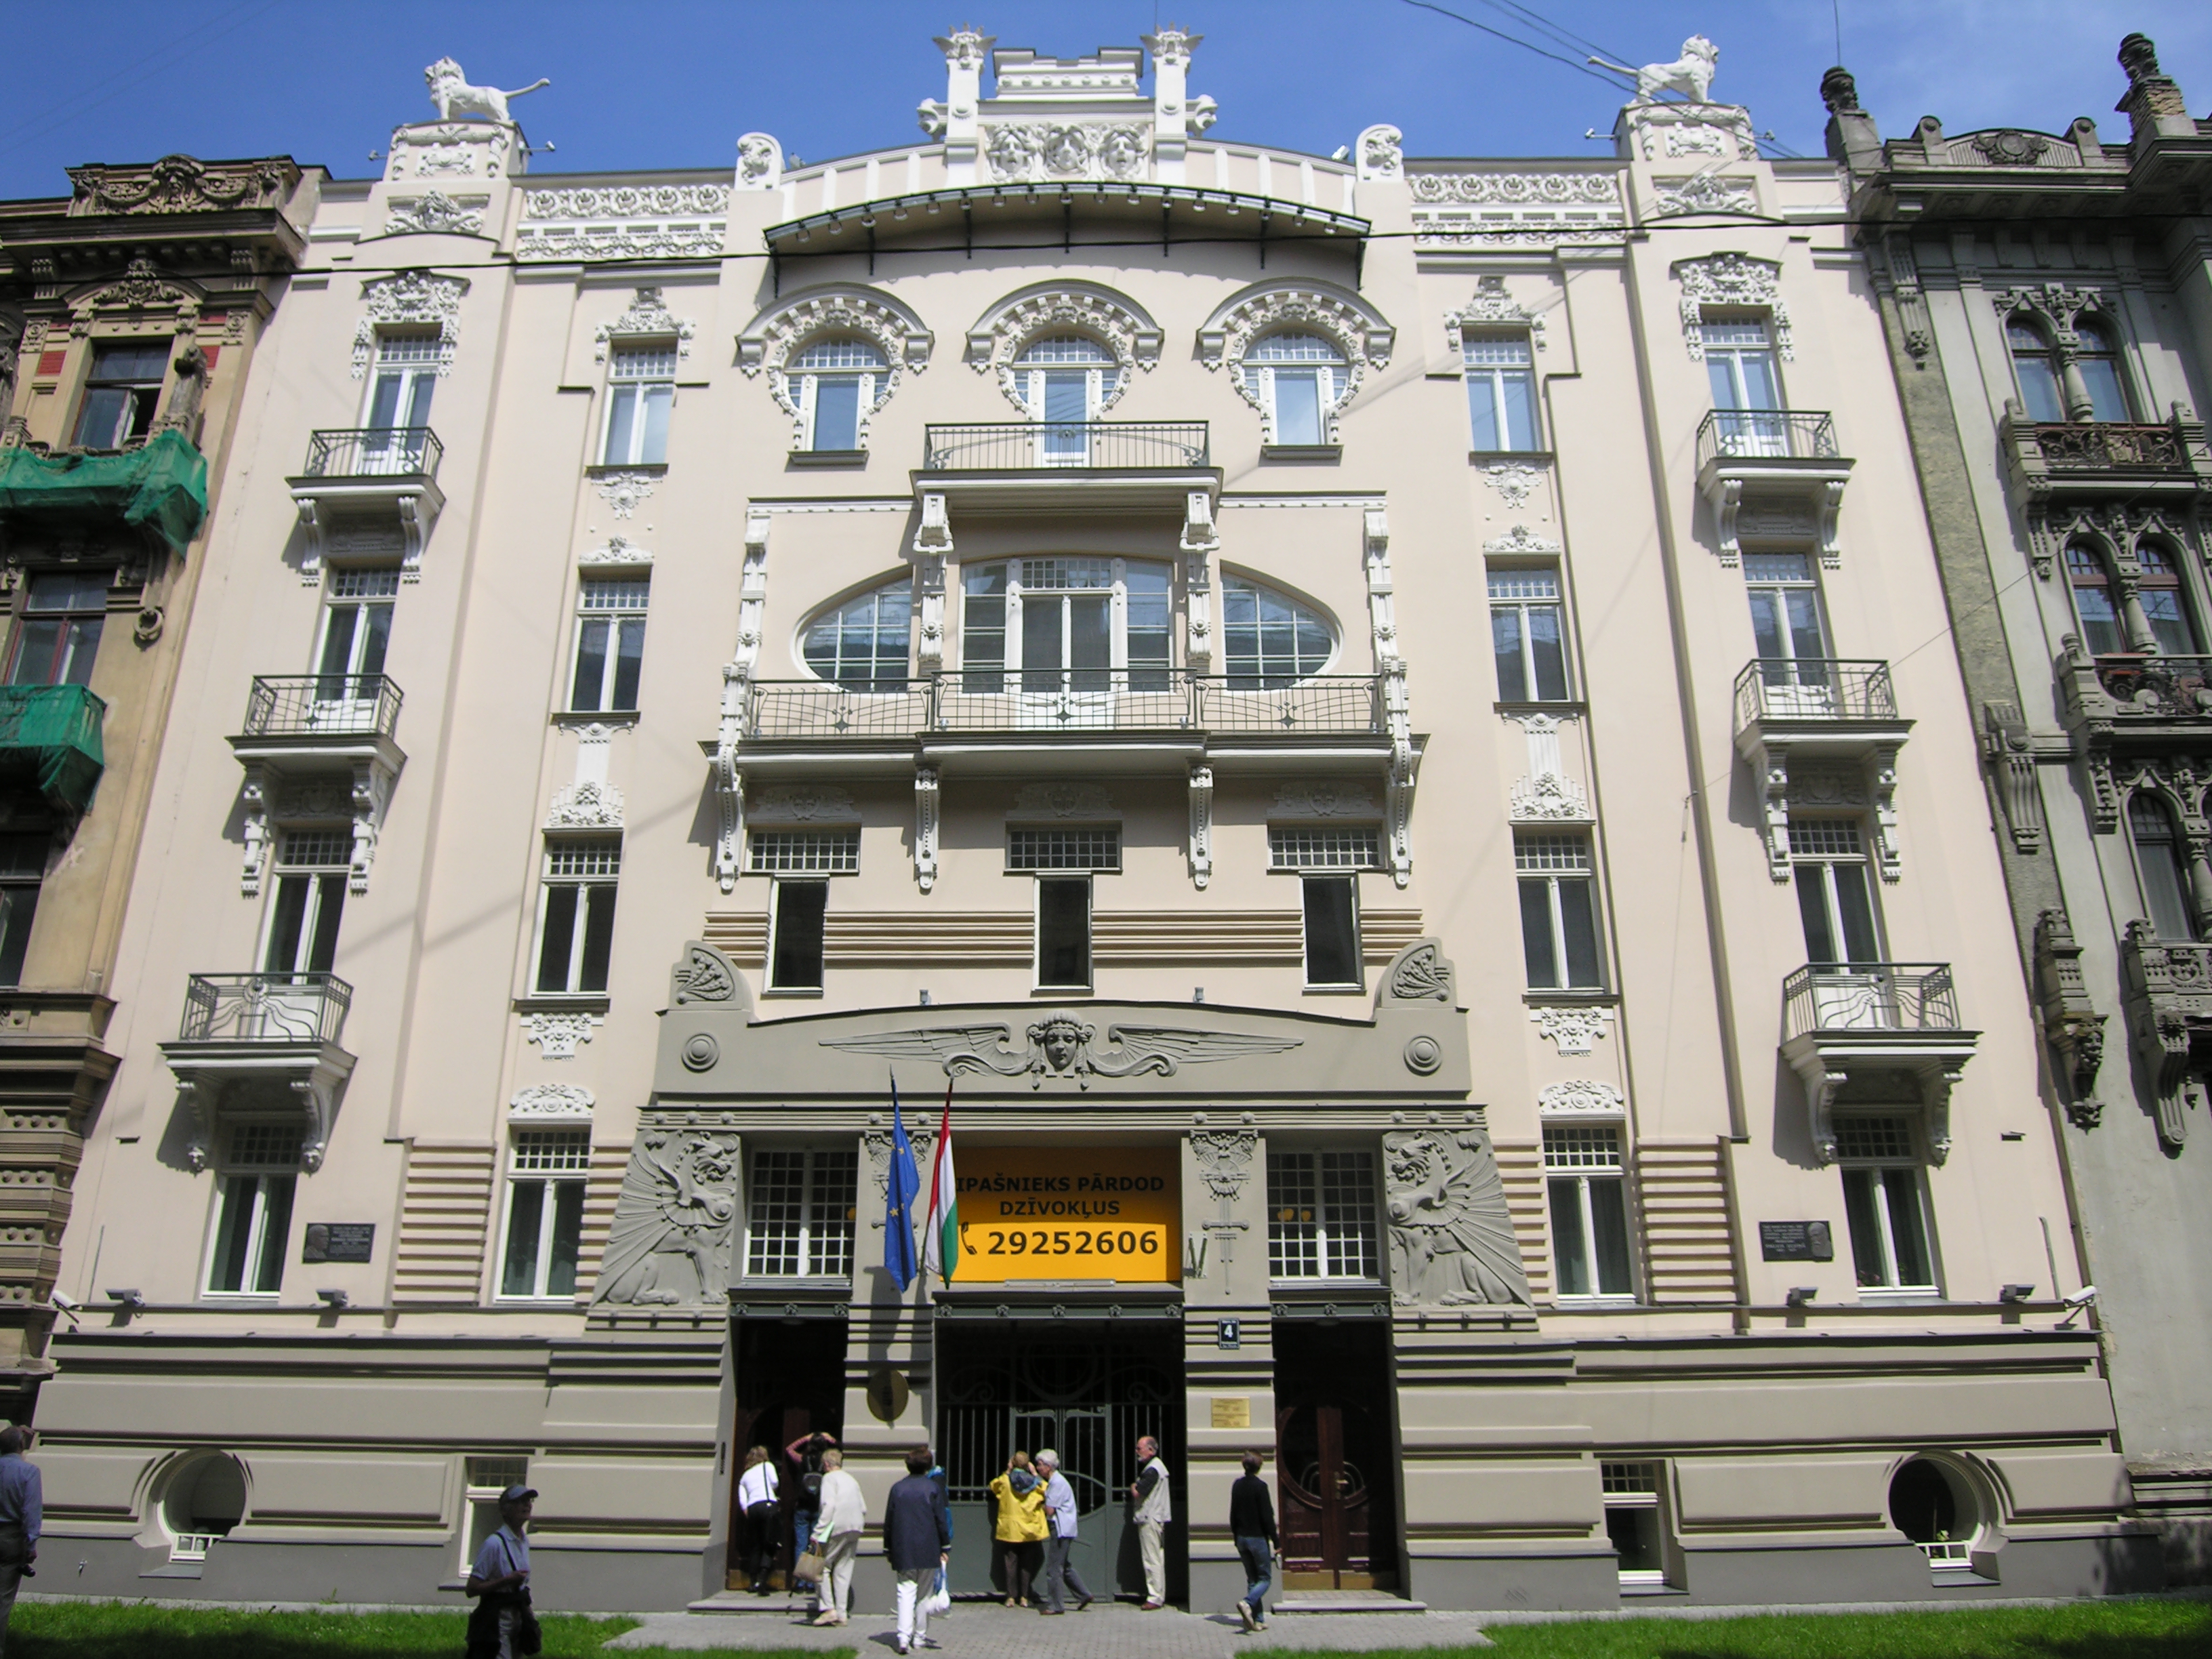
[For no reason whatsoever, totally unconnected; Riga Jugendstil]

Note to self: GDPR scrum with or without the r

Just to remind myself, and you for your contributions, that it’s seriously time to write up a post on Agile development methods [OK, okay, I mean Scrum, as the majority side of the house]; how one is supposed to integrate GDPR requirements into that.
Like, we’re approaching the stage where the Waterfall model      of security implementation, will be Done for most organisations. Not Well Done, rather Rare or Pittsburg Rare, at your firm [not Firm …]. But then, we’ll have to make the wholesale change to Maintenance, short-term and long-term. And meanwhile, waterfall has been ditched for a long time already in core development work, hence we have a backlog (huh; the real kind) qua security integration (sic; the bolt-on kind doesn’t work anyway) into all these Agile Development methods of which word has it everyone and their m/br-other seems to make use these latter days.

But then, the world has managed to slip security into that. Which is praiseworthy, and needs more Spread The Word.

And then, there’s the GDPR. May we suggest to include it in ‘security’ as requirements flow into the agile development processes ..?
As said, I’ll expand on this l8r.
If only later, since we need to find a way to keep the DPOs out of this; the vast majority (sic) of them, with all due [which hence may be severely limited] respect, will not understand to a profound level they’ll try to derail your development even without the most basic capability to self-assess they do it, in ways that are excruciatingly hard to pinpoint, lay your finger on.

But as written, that’s for another time. In the meantime, I’d love to see your contributions (if/when serious) overflowing my mailbox… Plus:
[Lawyers lurking next door…; Zuid-As Ams]

Emergent logic

Some time ago I posted something(s) on how the audit community could become relevant again, veering away from compliance(-only or -not even a bit by the disclaimers that destroy a rainforest on every occasion) and moving into the world of ‘ethicality audits’ on autonomous decision( system)s.
Now with the insight that until now, the humans in the loop, the big loop with many steps of analysis to be taken, were as a matter of fact complicit in drafting and applying patterns and pattern matching techniques.
Which is no news, but when we see now the automated-logic type of decision making that is no more than a black box, the question is: How can we analyse what happens inside ..? Answer: Use the tools that Big Data analysts use; extend them to cover specific cases / transactions and see how the argumentation flow was.    ..?

Still, there may be progress in this way. E.g., by the ‘decision’ or behaviour of the system, being emergent. So that we don’t focus on the bits (almost literally) of the case at hand but on the meaning of those bits. Because that’s the level that ‘conscious’ reasoning works on, seeking the nous from the lower and material levels, working on the ‘machine’ at the higher level, and then translating it back to the material outcome.
Which is similar to the analysis that is Process Analysis, if done properly.

I’ll expand, later. And:
[Aranjuez to impress; same]

The privacy-nightmare not your pseudo-dreams

Again, some serious flaw in the GDPR: Its reliance on, sponsorship for, pseudonymisation.
Which is worthless, already against break-ins.
And is worse, much worse, when you consider all the exemptions for ‘statistical use’ that are a cover for all the blatant abuse of personal data that the GDPR was originally intended to counter. And is worse, because six publicly available data points are all that is needed to identify anyone of the general public. De-anonymisation may be an art of sorts, but not a difficult one; easily demonstrated by any half-ass capable “hacker” consultant involved. [Of the Real kind]

Outside the controllers/processors conglomerates, such six points may have to be searched for – holdit; done. – but when anyone were to be able to infiltrate (why haven’t we heard of APTs for so long now? Because it was the TLAs, or is the overall picture waaayyy too scary to consider?), those six points are often found winthin one data set, if not with the IDs in some hardly-remote table.

And don’t come with the solution of homomorphic encryption, so usable for the statistical stuff. Also cracked, ever more systemically.

As if in today’s 21st century age, anyone would come forward with ‘these new developments, of motorised aeroplanes, with a “propellor” and all; they hold a promise for possible trans-atlantic flight!’ — Yet the GDPR isn’t different…

And:
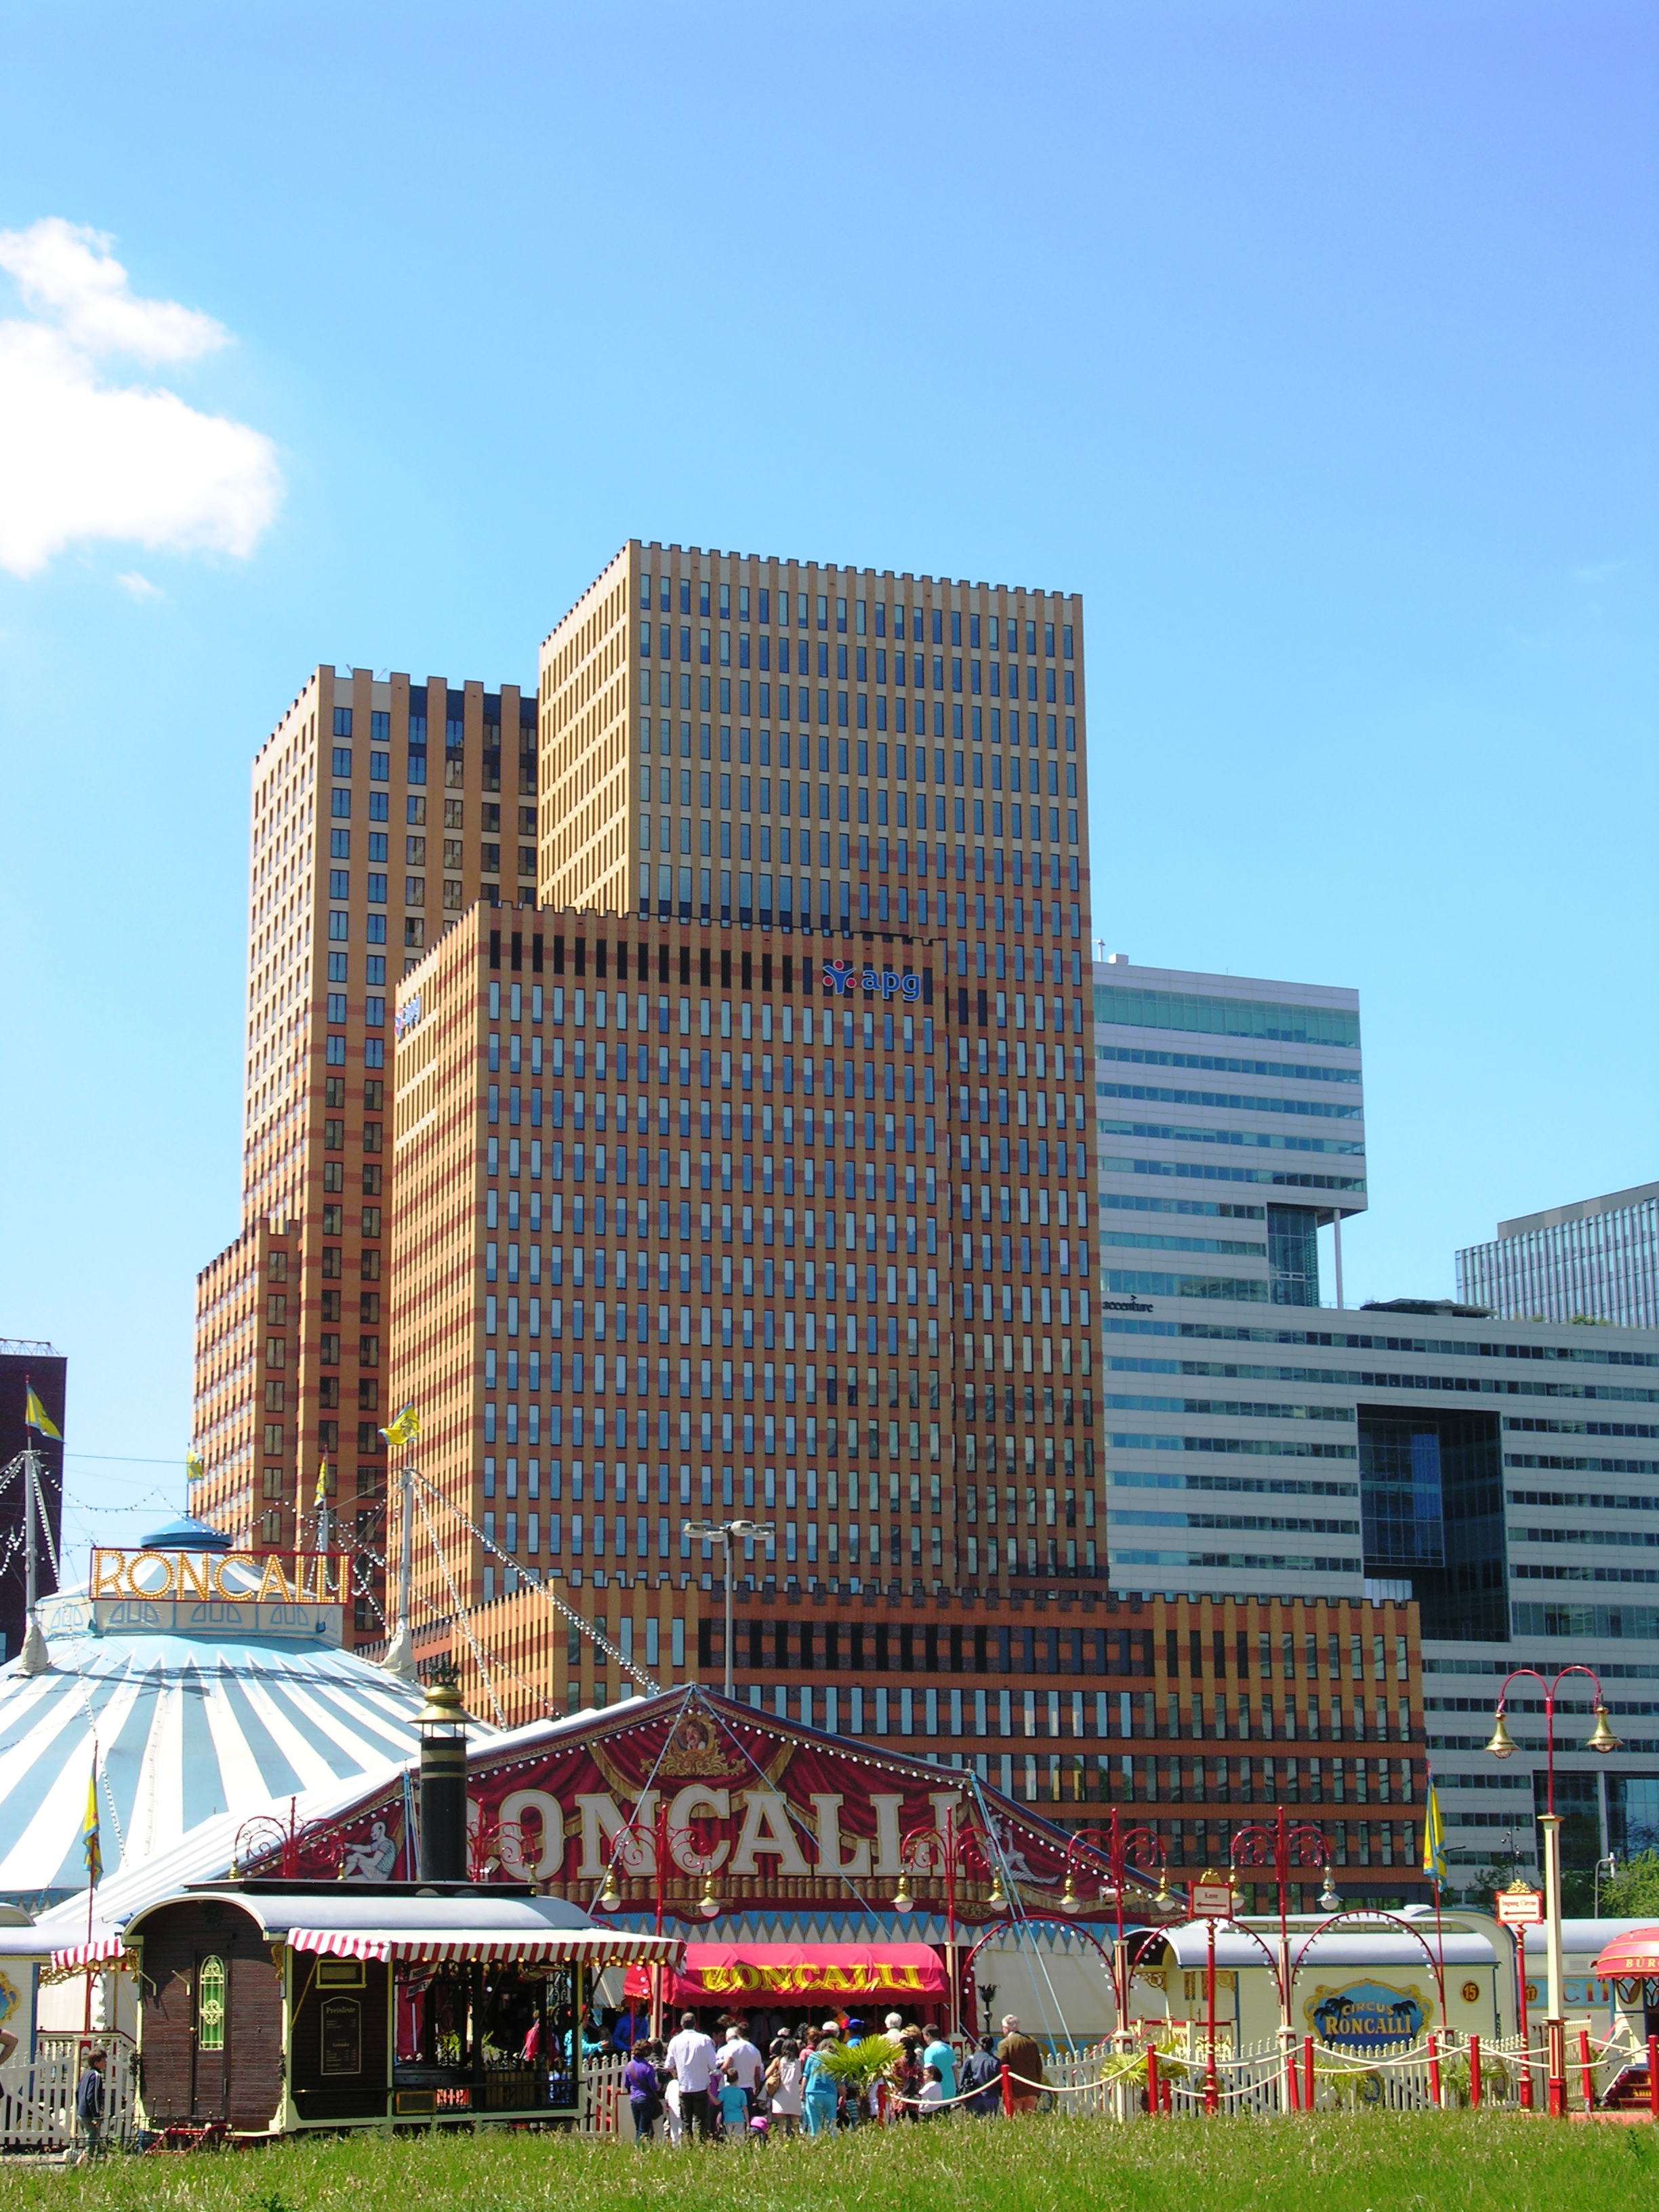
[The background has much more circus than the tent before it, ifyaknowaddImean; Zuid-As Ams]

Music to AI’s ears

Will AI eventually appreciate music ..?

Not just appreciate in a sense of experiencing the quality of it — the latter having ‘technical’ perfection as its kindergarten basement’s starting level only; where the imperfections are cherishable as huge improvements, yes indeed [Perfection Is Boring!] … but moreover, music appreciation having a major element of recognition, subconsciously mostly, of memories of times almost-im-memorial.

Of course, the kindergarten perfection gauging, AI will be able to do easily. Will, or does; simple near-algorithmic A”I” can do that today.

Appreciating imperfections, the same, with a slight randomiser (-recogniser) thrown in the algo mix.

But the recollection part, even at a conscious level requires memories to be there, and as far as AI goes (today) even ASI will have different memory structures since the whole facts learning processes are different. And don’t mention the subconscious side.

Yes, ASI can have a subconscious, of which we aren’t aware of even able to be aware [Note to self: to cover in audit philosophy development]. But when we don’t hear of this, was there a tree that fell in the forest?

I’m off some tangent direction.

What I started out to discuss is: At what point does music appreciation through the old(est) memories recall, become an element of ‘intelligence’ ..?

With the accompanying question, on my priority list when discussing AxI: Is it, for humans ..?

And a bonus question: Do you really think that AI would prefer, or learn earlier about the excellence, of Kraftwerk or Springsteen? Alas, your first response was wrong; Kraftwerk’s the kind of subtle intelligent hint-laden apparently-simple stuff that is very complex and also deeply human — which you perceive only when listening carefully over and over again till you get the richness and all the emotions (there they are!) and yearning for the days gone by when the world was a better place. Springsteen, raw and Original-Forceful on the surface — but quickly showing a (rational-level) algorithmics play with not as much depth; even the variations and off-prefection bits are well thought-out, leaving you with much less relatable memories if at all.

Your thoughts are appreciated. And:
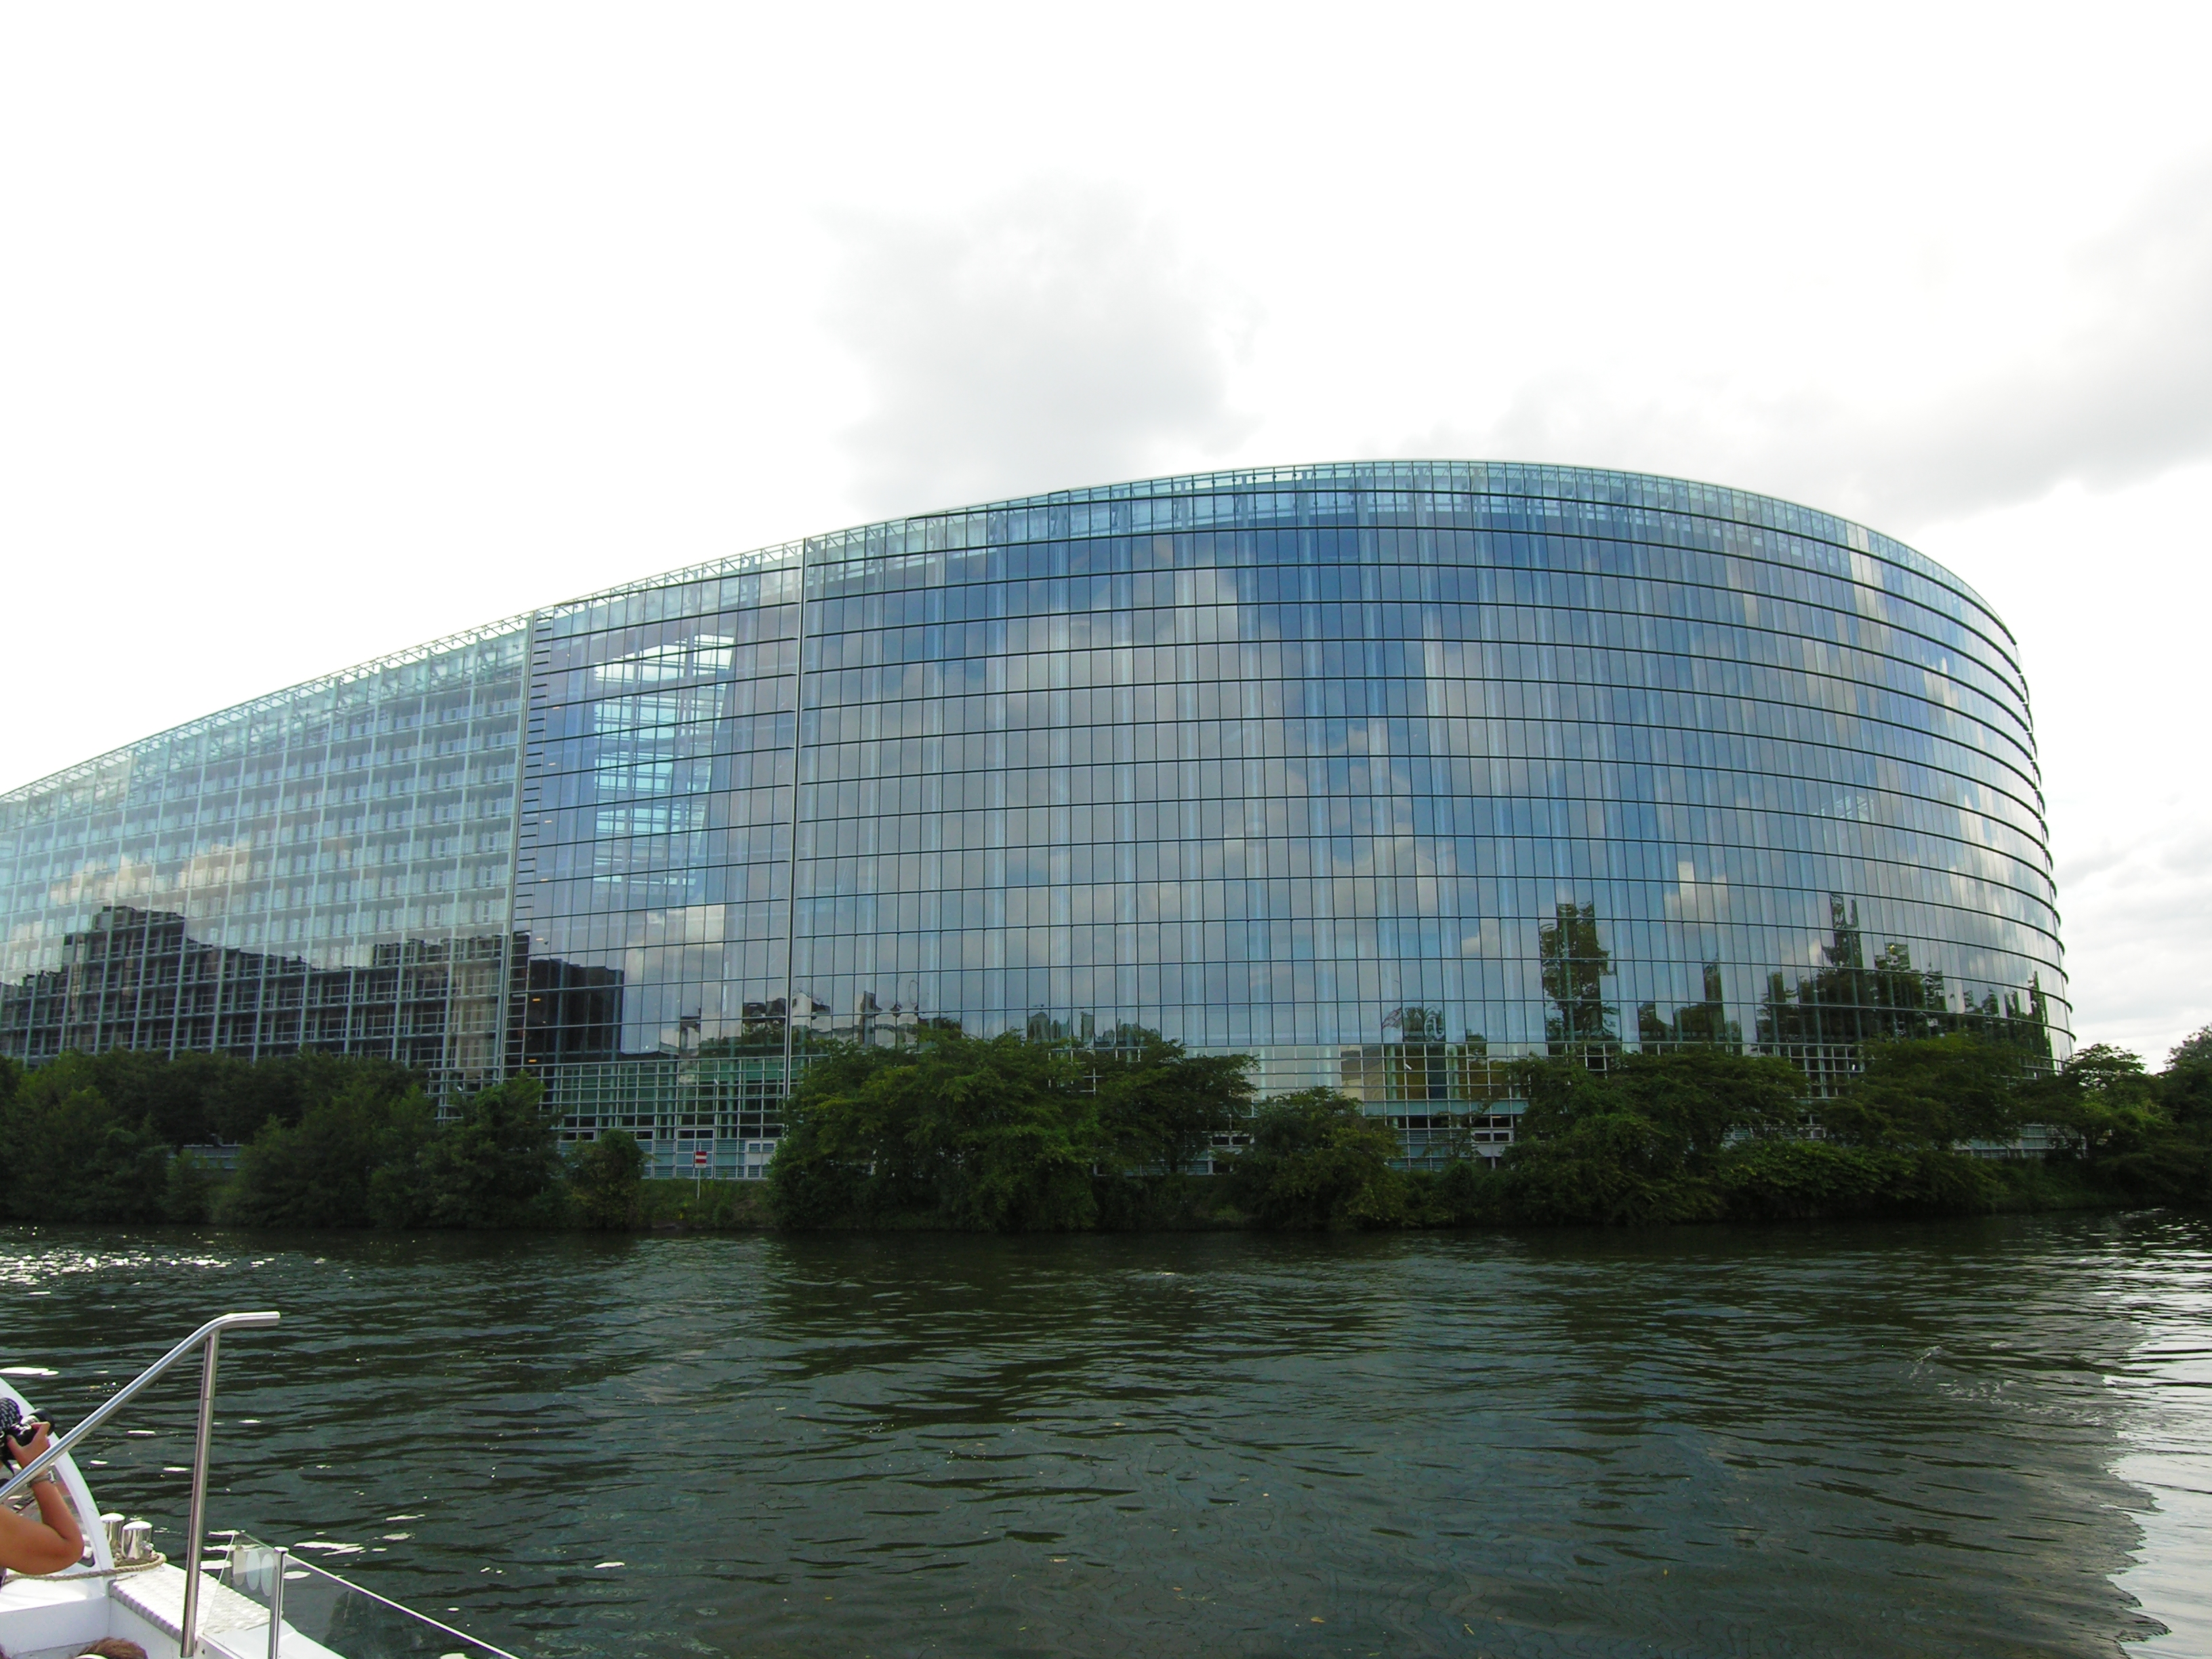
[Appropriately seemingly transparent but completely opaque; some EU parliament (?), Strassbourg]

Maverisk / Étoiles du Nord